Joel Callicrate
Joel Callicrate Cybersecurity AI researcher

Engineering for an Internet that doesn't play nice

Cybersecurity AI researcher and engineering leader

I lead small teams building AI-assisted security systems for noisy, adversarial environments. I work with analysts, engineers, product teams, and partners to ship those systems.

Selected work

Security systems I've built

Examples from threat intelligence, detection engineering, and child safety. Details are sanitized.

CASE 01 Threat intelligence Global spamtrap footprint
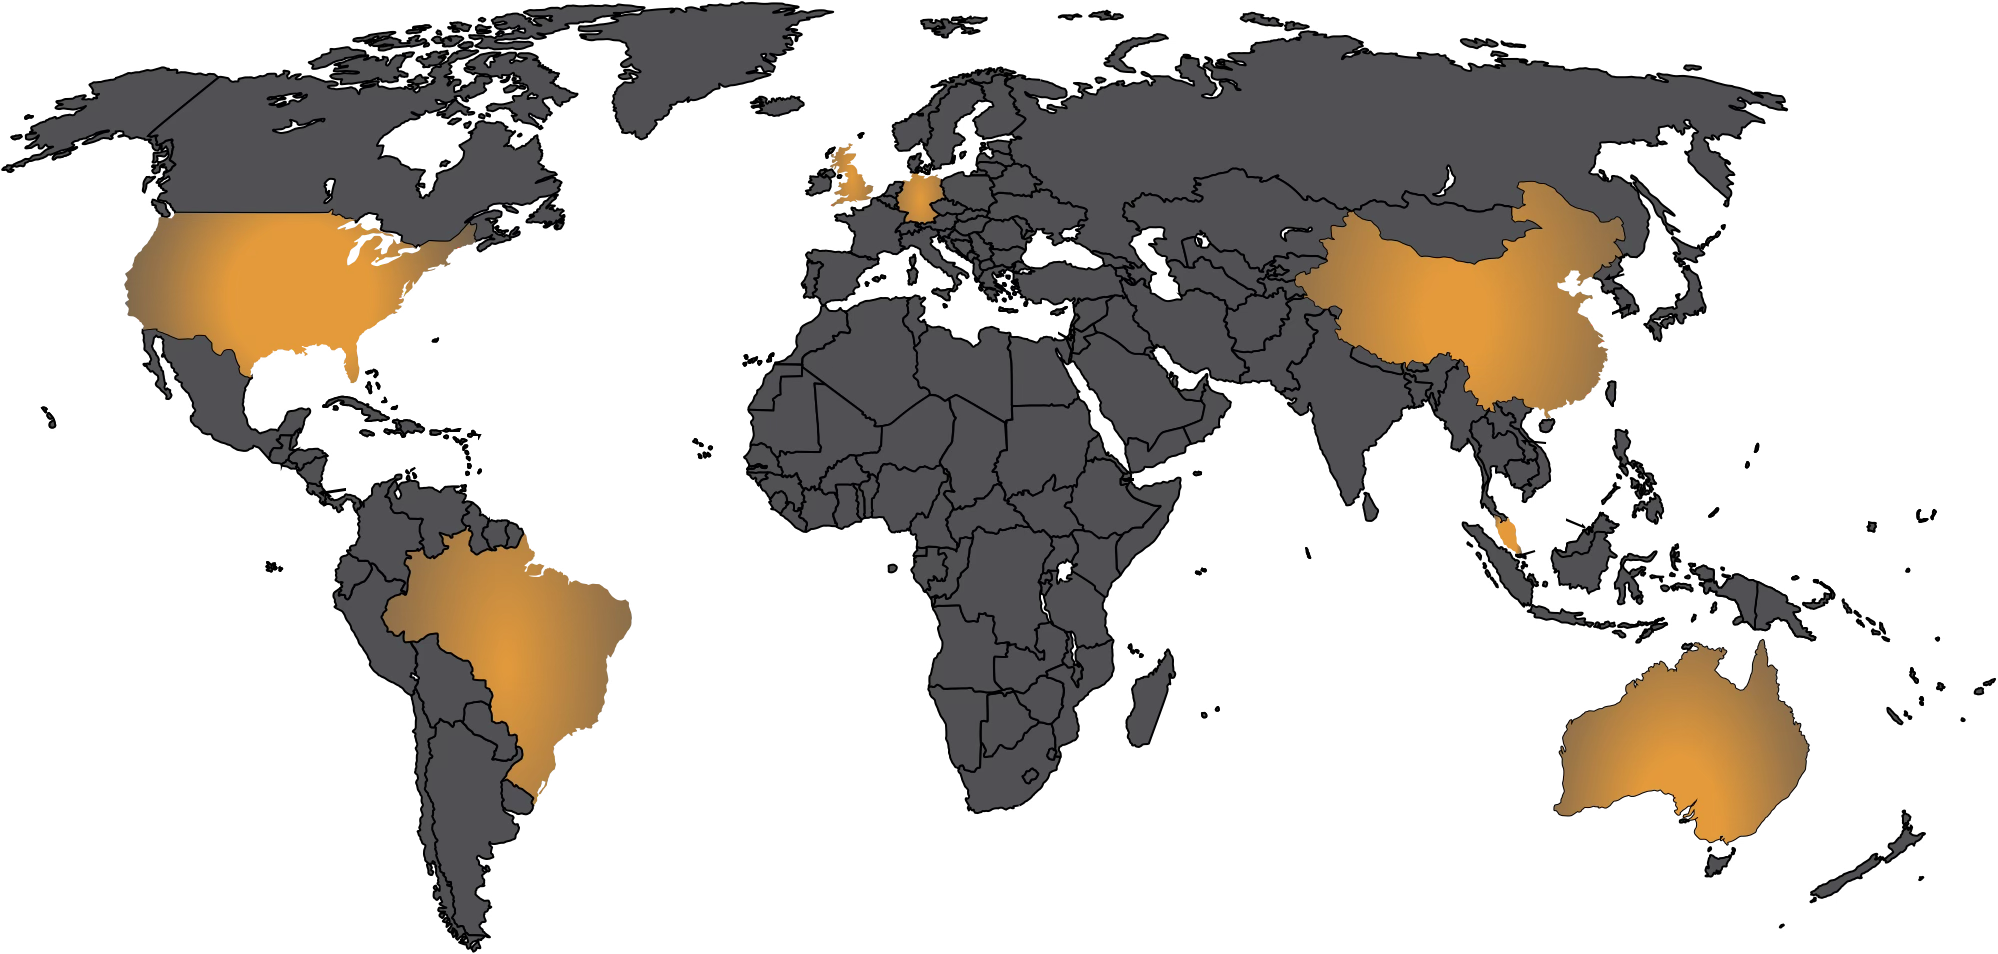
World map highlighting global spamtrap coverage across multiple regions

Expanding Threat Visibility

Problem

Detection teams could see only fragments of adversarial email campaigns.

Solution

Designed and operated a Databricks-based spamtrap pipeline to collect and analyze a continuous, high-volume stream of campaign telemetry.

→ ~30× increase in campaign visibility
→ Continuous adversarial telemetry
↑ Top
CASE 02 Gen-AI tooling Closed-loop rule generation
Ticket intake
Gen-AI rule generation
Deterministic validation
Analyst feedback

Accelerating Detection Response

Problem

The support desk needed a way to convert campaign evidence into detection coverage that was fast, repeatable, and didn't escalate every case to engineering.

Solution

Built a foundation-model rule generator with deterministic validation, structured feedback, and dynamic content enrichment. Rule-based checks validated the generated rules for production use.

→ Cut resolution time by 65%
→ Fewer escalations to engineering
↑ Top
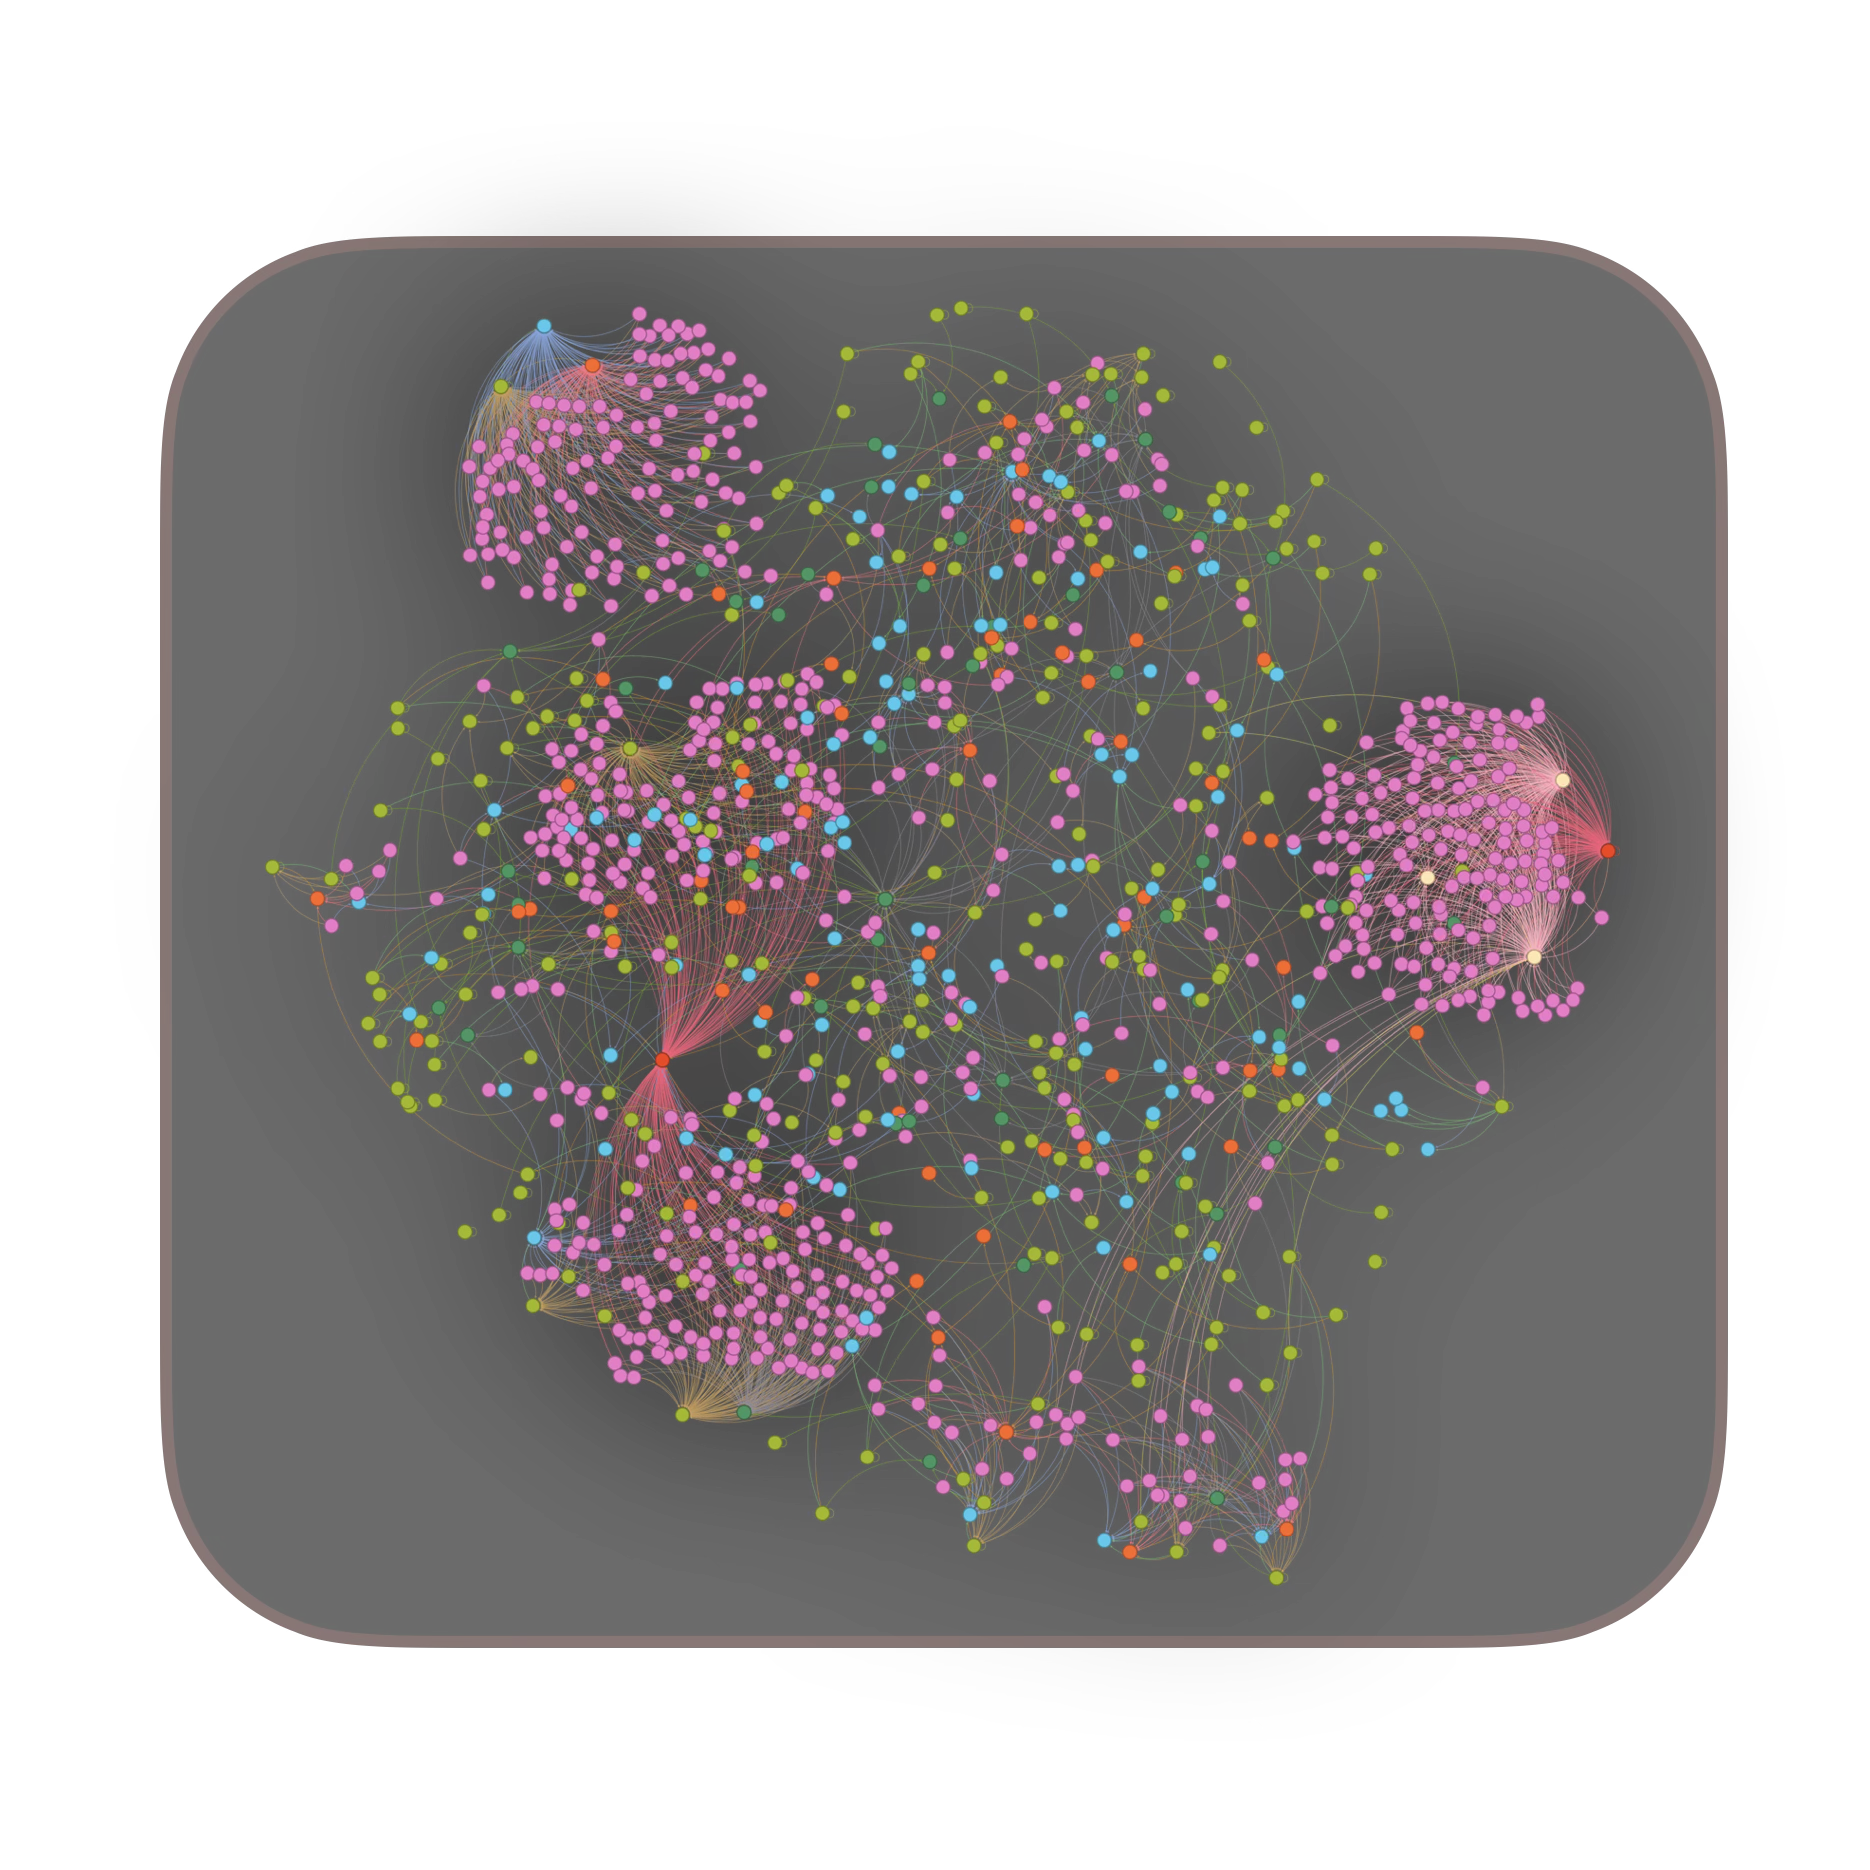
CASE 03 Trust & safety Correlated abuse infrastructure
Network graph visualization of correlated abuse infrastructure

Supporting Global Child Safety

Problem

Online abuse networks rapidly shift infrastructure to evade detection. Static signatures and one-off takedowns can't keep up.

Solution

Analyzed telemetry to connect related accounts, domains, and infrastructure, then turned those patterns into detections partners could act on as networks changed.

Supporting
↑ Top
Background

Two decades in software and security

I've worked on software-defined radio, infrastructure emulation, and AI-assisted detection.

2019–Present

Cybersecurity AI Researcher

Cisco Talos

  • AI / LLM pipelines
  • Attribution at scale
  • Detection engineering
2014–2019

Principal Engineer

Feather Information Technology, Government Programs

  • Infrastructure emulation
  • Multi-stage attack workflows
  • Rapid-response tooling
2013–2014

Systems Engineering Technical Advisor (SETA)

TASC

  • Tactical SDR architecture
  • ~$20M program
  • Signal processing pipelines
2007–2013

Senior Software Engineer

Lockheed Martin

  • Large-scale deployment
  • Lifecycle automation
2004–2007

Web Developer

State of Oregon

  • Web automation
  • Input validation
2000–2003

Technical Assistant

Dallas School District #2

  • Sysadmin
  • End-user support
Notable
Education
  • MS, Cybersecurity Johns Hopkins University
  • BS, Computer Science Oregon State University
When I'm not at a terminal
  • 12 yrs coaching K–8 soccer
  • 9 yrs mentoring middle-school students in my church youth group
Writing

A Second Look

Notes on software, security, AI, and measurement. I update them when I find better evidence.

Contact

Let's talk.

I'd love to hear what you're working on, especially if it involves adversarial data, large-scale detection, AI-assisted investigation, or production systems that need to hold up under pressure.

Columbia, MD hello@grayarea.dev